Enhance your career with CAS-004 PDF Dumps – True CompTIA Exam Questions [Q300-Q323]

Rate this post

Enhance your career with CAS-004 PDF Dumps – True CompTIA Exam Questions

New (2025) Download free CAS-004 PDF for CompTIA Practice Tests

NEW QUESTION 300
A security auditor needs to review the manner in which an entertainment device operates. The auditor is analyzing the output of a port scanning tool to determine the next steps in the security review. Given the following log output.
The best option for the auditor to use NEXT is:


NEW QUESTION 301
A security analyst wants to keep track of alt outbound web connections from workstations. The analyst’s company uses an on-premises web filtering solution that forwards the outbound traffic to a perimeter firewall. When the security analyst gets the connection events from the firewall, the source IP of the outbound web traffic is the translated IP of the web filtering solution. Considering this scenario involving source NAT. which of the following would be the BEST option to inject in the HTTP header to include the real source IP from workstations?


NEW QUESTION 302
Due to internal resource constraints, the management team has asked the principal security architect to recommend a solution that shifts partial responsibility for application-level controls to the cloud provider. In the shared responsibility model, which of the following levels of service meets this requirement?


NEW QUESTION 303
A security architect examines a section of code and discovers the following:

Which of the following changes should the security architect require before approving the code for release?


NEW QUESTION 304
Which of the following technologies should the company deploy to meet its security objectives? (Select TWO)_


NEW QUESTION 305
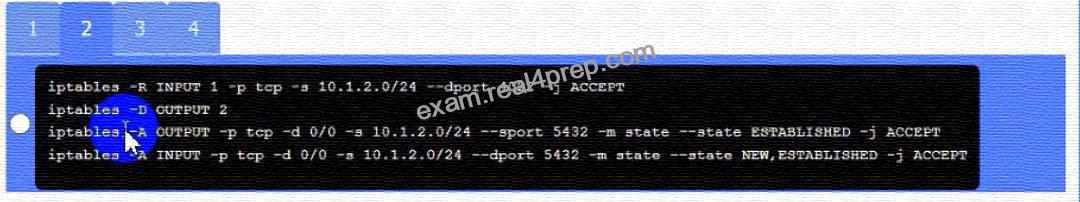
A security engineer needs to review the configurations of several devices on the network to meet the following requirements:
* The PostgreSQL server must only allow connectivity in the 10.1.2.0/24 subnet.
* The SSH daemon on the database server must be configured to listen
to port 4022.
* The SSH daemon must only accept connections from a Single
workstation.
* All host-based firewalls must be disabled on all workstations.
* All devices must have the latest updates from within the past eight
days.
* All HDDs must be configured to secure data at rest.
* Cleartext services are not allowed.
* All devices must be hardened when possible.
Instructions:
Click on the various workstations and network devices to review the posture assessment results. Remediate any possible issues or indicate that no issue is found.
Click on Server A to review output data. Select commands in the appropriate tab to remediate connectivity problems to the pOSTGREsql DATABASE VIA ssh

WAP A

PC A

Laptop A

Switch A

Switch B:

Laptop B

PC B

PC C

Server A


NEW QUESTION 306
A company security engineer arrives at work to face the following scenario:
1) Website defacement
2) Calls from the company president indicating the website needs to be fixed Immediately because It Is damaging the brand
3) A Job offer from the company’s competitor
4) A security analyst’s investigative report, based on logs from the past six months, describing how lateral movement across the network from various IP addresses originating from a foreign adversary country resulted in exfiltrated data Which of the following threat actors Is MOST likely involved?


NEW QUESTION 307

NEW QUESTION 308
A company wants to protect its intellectual property from theft. The company has already applied ACLs and DACs.
Which of the following should the company use to prevent data theft?


NEW QUESTION 309
A network administrator receives a ticket regarding an error from a remote worker who is trying to reboot a laptop. The laptop has not yet loaded the operating system, and the user is unable to continue the boot process.
The administrator is able to provide the user with a recovery PIN, and the user is able to reboot the system and access the device as needed. Which of the following is the MOST likely cause of the error?


NEW QUESTION 310
Which of the following processes involves searching and collecting evidence during an investigation or lawsuit?


NEW QUESTION 311
An organization is planning for disaster recovery and continuity of operations.
INSTRUCTIONS
Review the following scenarios and instructions. Match each relevant finding to the affected host.
After associating scenario 3 with the appropriate host(s), click the host to select the appropriate corrective action for that finding.
Each finding may be used more than once.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.

NEW QUESTION 312
Which of the following is a risk associated with SDN?


NEW QUESTION 313
Law enforcement officials informed an organization that an investigation has begun. Which of the following is the FIRST step the organization should take?


NEW QUESTION 314
A new requirement for legislators has forced a government security team to develop a validation process to verify the integrity of a downloaded file and the sender of the file Which of the following is the BEST way for the security team to comply with this requirement?


NEW QUESTION 315
An attacker infiltrated an electricity-generation site and disabled the safety instrumented system. Ransomware was also deployed on the engineering workstation. The environment has back-to-back firewalls separating the corporate and OT systems. Which of the following is the MOST likely security consequence of this attack?


NEW QUESTION 316
A recent data breach revealed that a company has a number of files containing customer data across its storage environment. These files are individualized for each employee and are used in tracking various customer orders, inquiries, and issues. The files are not encrypted and can be accessed by anyone. The senior management team would like to address these issues without interrupting existing processes.
Which of the following should a security architect recommend?


NEW QUESTION 317
A city government’s IT director was notified by the city council that the following cybersecurity requirements must be met to be awarded a large federal grant:
– Logs for all critical devices must be retained for 365 days to enable monitoring and threat hunting.
– All privileged user access must be tightly controlled and tracked to
mitigate compromised accounts.
– Ransomware threats and zero-day vulnerabilities must be quickly
identified.
Which of the following technologies would BEST satisfy these requirements? (Choose three.)


NEW QUESTION 318
A security manager is creating a standard configuration across all endpoints that handle sensitive dat a. Which of the following techniques should be included in the standard configuration to ensure the endpoints are hardened?


NEW QUESTION 319
A security analyst is reviewing the following output:

Which of the following would BEST mitigate this type of attack?


NEW QUESTION 320
An administrator at a software development company would like to protect the integrity Of the company’s applications with digital signatures. The developers report that the signing process keeps failing on all applications. The same key pair used for signing, however, is working properly on the website, is valid, and is issued by a trusted CA. Which of the following is MOST likely the cause of the signature failing?


NEW QUESTION 321
A small company recently developed prototype technology for a military program. The company’s security engineer is concerned about potential theft of the newly developed, proprietary information.
Which of the following should the security engineer do to BEST manage the threats proactively?


NEW QUESTION 322
An organization is designing a network architecture that must meet the following requirements:
Users will only be able to access predefined services.
Each user will have a unique allow list defined for access.
The system will construct one-to-one subject/object access paths dynamically.
Which of the following architectural designs should the organization use to meet these requirements?


NEW QUESTION 323
A large organization is planning to migrate from on premises to the cloud. The Chief Information Security Officer (CISO) is concerned about security responsibilities. If the company decides to migrate to the cloud, which of the following describes who is responsible for the security of the new physical datacenter?


CompTIA Advanced Security Practitioner (CASP+) certification exam, also known as CAS-004, is a globally recognized certification that validates advanced-level security skills and knowledge. The CASP+ certification is designed for IT professionals who have at least ten years of experience in IT administration, including five years of hands-on experience in technical security roles. CompTIA Advanced Security Practitioner (CASP+) Exam certification exam covers a broad range of advanced security topics such as risk management, enterprise security architecture, research and collaboration, and integration of security controls for heterogeneous systems. The CASP+ certification is highly valued by employers as it demonstrates that the individual has the necessary skills and knowledge to lead and manage complex security projects.

The CompTIA CAS-004 exam consists of 90 multiple-choice and performance-based questions, which must be completed within 165 minutes. CAS-004 exam is available in English, Japanese, and Portuguese, and is delivered through Pearson VUE testing centers worldwide. The passing score for the CASP+ exam is 750 on a scale of 100-900.


100% Free CAS-004 Files For passing the exam Quickly: https://www.real4prep.com/CAS-004-exam.html


Related Links: www.stes.tyc.edu.tw myportal.utt.edu.tt www.stes.tyc.edu.tw myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt

Related Posts

Verified DY0-001 exam dumps Q&As with Correct 85 Questions and Answers [Q37-Q54]

Verified DY0-001 exam dumps Q&As with Correct 85 Questions and Answers CompTIA DY0-001 Test Engine PDF – All Free Dumps from Real4Prep CompTIA DY0-001 Exam Syllabus Topics:…

[Aug 10, 2026] CS0-003 Ultimate Study Guide – Real4Prep [Q122-Q138]

[Aug 10, 2026] CS0-003 Ultimate Study Guide – Real4Prep Ultimate Guide to Prepare CS0-003 Certification Exam for CompTIA Cybersecurity Analyst in 2026 CompTIA CS0-003 exam is designed…

[Mar 12, 2026] XK0-005 Exam Dumps, XK0-005 Practice Test Questions [Q339-Q361]

[Mar 12, 2026] XK0-005 Exam Dumps, XK0-005 Practice Test Questions Free XK0-005 Study Guides Exam Questions and Answer CompTIA Linux+ certification is vendor-neutral, which means that it…

[Jan-2026] Pass CV0-003 Exam in First Attempt Updated CV0-003 Exam Questions [Q234-Q249]

[Jan-2026] Pass CV0-003 Exam in First Attempt Updated CV0-003 Exam Questions CompTIA Cloud+ Dumps CV0-003 Exam for Full Questions – Exam Study Guide CompTIA CV0-003 exam is…

Latest [Apr 10, 2025] CompTIA CV0-003 Real Exam Dumps PDF [Q113-Q137]

Latest [Apr 10, 2025] CompTIA CV0-003 Real Exam Dumps PDF CV0-003 Practice Test Questions Updated 464 Questions CompTIA CV0-003 Exam Syllabus Topics: Topic Details Topic 1 Cloud…

Free CS0-002 Exam Braindumps certification guide Q&A [Q69-Q93]

Free CS0-002 Exam Braindumps certification guide Q&A CS0-002 Certification Overview Latest CS0-002 PDF Dumps The Best CompTIA CS0-002 Study Guides and Dumps of 2024: https://www.real4prep.com/CS0-002-exam.html    …

發佈留言

發佈留言必須填寫的電子郵件地址不會公開。 必填欄位標示為 *

输入下图中的文字